
GitHub Copilot Code Review: New policy APIs and MCP attribution—what they actually prove
GitHub adds API-managed Copilot code review settings. An original analysis of enterprise and repository rights, MCP attribution, AI credits and review limits.
1. AI review becomes an administrative control plane
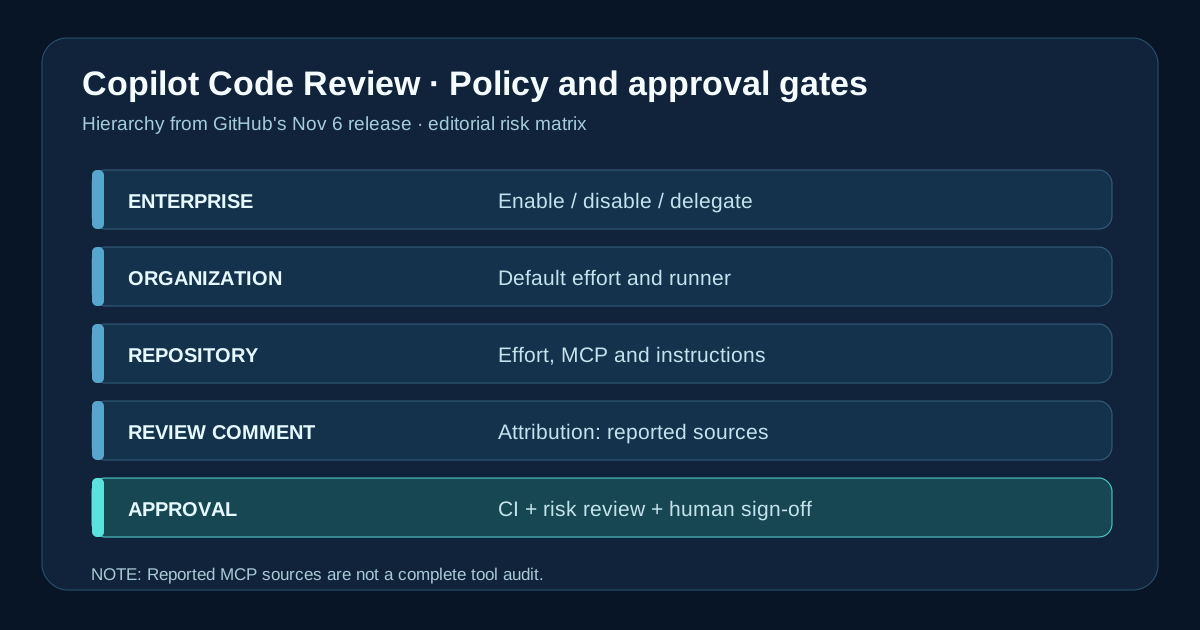
GitHub's November 6 update matters because organizations increasingly operate AI code review as a managed service. Enterprise administrators can allow, prohibit or delegate reviews. Organization administrators can manage enablement, default review effort and runner configuration. Repository administrators control effort and the use of custom instructions and MCP tools. Enterprise-managed settings cannot be overridden at lower levels.
2. What attribution actually demonstrates
GitHub exposes explicit review and comment attribution, review effort when the field is available, and reported sources such as skills, MCP servers and custom instructions.
AgentenCode analysis: This context helps locate unexpected dependencies. A tool mentioned as a source does not prove that every execution was captured in a tamper-evident log, that all permissions were enforced or that the code finding is correct. Critical release workflows still need independent rights enforcement, CI results and human approval.
3. Role and token matrix
| Scope | New control | Key restriction |
|---|---|---|
| Enterprise | Review enable/disable or delegation | Central policy prevails |
| Organization | Enablement, default effort, runner | No override of enterprise policy |
| Repository | Effort, instructions and MCP use | Repository admin authorization |
| Review metadata | Attribution and reported tools | Not a complete tool audit |
| Agent session | Credits consumed | Not a fixed price |
Authentication caveat: GitHub says enterprise and organization settings endpoints, including the organization runner endpoint, do not support GitHub Apps or fine-grained PATs. Repository settings endpoints do support both, with Administration: read to read or Administration: write to change settings. Classic PATs require repository administrator access. Teams cannot assume one app token works at every tier.
4. Credits, retries and model selection
The session can display AI credits consumed. That does not establish a universal price per review. GitHub says failed or timed-out reviews are retried once; another eligible model can be used if the preferred one is unavailable. Teams should collect review ID, effort, applicable policy, credits, retries and the human decision rather than treat raw AI review counts as proven quality.
5. More compact results are not more complete results
The overview consolidates skipped and excluded paths in Files not reviewed, with reasons. Findings unrelated to later changes can be deemphasized. According to GitHub, Balanced effort uses three reviewer models with another model combining their findings. This may speed triage, but it does not mean excluded files were examined or that any finding was independently validated.
6. Original AgentenCode approval matrix
| Situation | Necessary control | Insufficient evidence |
|---|---|---|
| Automatic review enabled | Enterprise/org policy plus bypass rules | Repo toggle alone |
| MCP tool allowed | Audit actual tool permissions | Comment attribution alone |
| No findings | CI, tests and risk-based human review | 0 findings |
| Excluded file | Assess omitted file risk | Compact overview |
| Credits charged | Track budget and retries | Assumed flat fee |
These are editorial operating recommendations, not a GitHub compliance certification.
7. Availability and a useful pilot
GitHub lists Copilot Pro, Pro+, Max, Business and Enterprise. Availability on these plans does not imply every user or token has admin access. A representative pilot should include sensitive changes, excluded paths and bot-authored PRs, tracking policy tier, effort, reported tools, credits, CI results and human disposition. Do not make autonomous merge decisions from AI summaries alone.
FAQ
Can a GitHub App configure all organization and enterprise settings? No, GitHub explicitly excludes Apps and fine-grained PATs from the announced settings endpoints at those levels.
Is MCP execution now fully auditable? There is extra attribution, but not proof of a complete, tamper-evident action log.
Can Copilot replace human security approval? The release supplies no such guarantee; testing and human review remain essential for consequential changes.
Do visible credits mean predictable total costs? Not necessarily; costs depend on actual use and plan terms.
Sources and limits
GitHub Changelog, Copilot code review: API management and review overview updates (November 6, 2026) and GitHub Docs: Configuring Copilot code review. Vendor statements are distinguished from editorial analysis. No independent API/permission testing, cost measurement or security certification by AgentenCode.
Primary sources and limitations
Primary-source reporting and original editorial analysis. No independent replication, agent safety certification, or universal availability/cost guarantees.