
Mistral Studio brings managed agents and workflows to enterprise infrastructure
An agent runtime and governance stack, not just another model
Studio combines managed agents, approvals, traces and evaluations. The practical question: which parts are public preview and which controls actually work in your deployment?
Agents, workflows and apps on shared infrastructure
On November 5, 2026, Mistral described an expansion of Mistral Studio designed to connect Managed Agents, Workflows and Apps on a common enterprise infrastructure. Agents may use skills, subagents, hooks and code sandboxes; workflows combine rules, reasoning and approvals; apps make those capabilities available to employees. The original Mistral Studio announcement sets out this direction.
The operational significance is that agent work is treated as an ongoing, inspectable process rather than an isolated chat. The vendor describes durable execution and visibility into tool calls and approvals. These are substantive engineering goals, but not proof that all configurations have passed an independent reliability or security audit.
Public preview is not the same as general availability
Mistral's November 5 release notes draw distinctions absent from a headline alone. Mistral-hosted Managed Agents are listed as public preview. Several new capabilities including offline and online evaluations, managed evaluation datasets and tracing for managed agents are likewise marked preview. By contrast, Studio Apps in Vibe Code Web is specifically labelled GA.
The vendor also describes deployment in its cloud, a private VPC, on-premises or hybrid environments. This is an architecture and commercial offering statement, not a blanket GA guarantee for every feature in every hosting arrangement. Enterprise teams need to check exact regions, identity options, traces and available functionality for their selected deployment.
AgentenCode operational control matrix
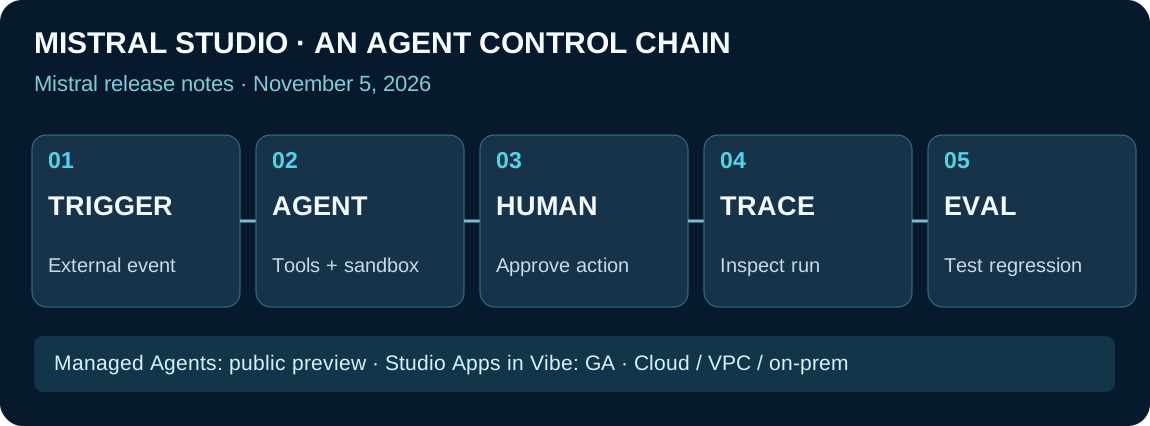
A practical operating chain is trigger → agent → human approval → trace → evaluation. Each link tests a separate failure mode: the event must be authentic, the tool invocation scoped, the consequential action approved, the history inspectable and the next version regression-tested.
| Component | Vendor status | Enterprise proof needed |
|---|---|---|
| Hosted Managed Agents | Public preview | Resume, access boundaries, retry behavior |
| Skills, subagents and sandboxes | Described in Studio launch | Test tool and child-agent privileges |
| Triggers and workflows | Announced features | Event authenticity, idempotency and approval |
| Tracing and evaluations | Several public-preview releases | Validate redaction, exports and actual test data |
| Studio Apps in Vibe Code Web | GA in release notes | Do not generalize that status to every Studio feature |
| Cloud, VPC and on-prem deployment | Vendor deployment design | Verify true data flows and product availability |
Data sovereignty must follow every connector
Mistral positions Studio as deployable in a customer's cloud, VPC, on-premises or a hybrid arrangement. The difference matters to institutions with strict data-residency requirements. Yet server geography is only one part of sovereignty. A meaningful audit traces documents, prompts, credentials, tool results, evaluation examples and diagnostic logs, not merely the model endpoint.
Our recommended inventory records each step's owner, data category, key material, tool permission, retention period, outbound destination and revocation method. A locally hosted model does not automatically ensure that an external connector or a managed trace service remains within the same jurisdiction.
Human approval and long-running jobs introduce new edge cases
Mistral says managed agents can run for extended periods, resume after interruptions and pause for human approval before a consequential action. For security teams, this creates additional questions. If approval arrives after the initiating user loses access, should the run continue? Can retried steps duplicate an irreversible action? Which operator can terminate the job?
A valuable pilot is a production-alert triage agent that reads a permitted runbook and creates an evidence-backed proposal but cannot execute the proposed fix without a separate approver. Deliberately interrupt one run and change a test user's privileges before resumption. The resulting behavior is a stronger control signal than a single smooth demo.
Observability and evaluations as reusable evidence
The Studio launch promises OpenTelemetry traces covering model use, tools and approvals. Release notes also describe default redaction for common secrets and personal data in hosted managed-agent tracing, together with ways to turn actual spans into curated evaluation datasets. Those claims need to be verified with the company's real sensitive fields and operational policies.
We would measure correctly authorized completions, blocked unauthorized operations and regressions under prompt, tool or model changes. Mistral's in-house productivity stories are useful ideas for pilot design but do not independently establish savings or safety for customer environments.
Our assessment and practical questions
AgentenCode assessment: The important innovation is bringing durable execution, approval checkpoints and testable trace evidence into an enterprise workflow. Hosting flexibility is a differentiator only when users can demonstrate their specific deployment's data and permission boundaries.
Are all Managed Agents capabilities GA? No. The November 5 hosted release is labelled public preview.
Can every component be installed on-premises? Mistral lists on-prem and VPC options, but the exact capabilities and commercial constraints must be confirmed per configuration.
Do vendor efficiency claims prove customer ROI? No. They are company-supplied examples, not independently reproduced benchmarks.
Sources, context and limitations
Primary sources: Mistral Studio original announcement and Mistral technical release notes, November 5. See the related Mistral Vibe Code dossier for an existing AgentenCode tool profile; it is not a separate Studio security evaluation.
Our editorial method compared per-feature release statuses against the broad announcement and developed an original failure-mode and approval matrix. No hands-on Studio deployment, on-prem test, independent security audit, or reproduced ROI evidence.
Keep exploring and verifying
Related existing profile: Mistral agent – dossier and evidence. This related profile does not constitute a test of the newly announced product.