
Amazon WorkSpaces adds user-bound access and session replay for AI agents
AWS adds OIDC sign-in, on-behalf-of identities and session replay for AI agents using managed cloud desktops. Explore Preview limits, privacy and enterprise controls.
Why agents need governed cloud desktops
On November 16, 2026, AWS announced new capabilities for WorkSpaces for AI Agents. The managed desktop service allows approved agents to operate existing ERP, CRM and other business applications through their interfaces. New features focus on identity, simpler setup and reconstructing agent activity for review.
WorkSpaces for AI Agents was already generally available earlier in 2026. The November announcement therefore extends an existing product rather than launching desktop automation for the first time. The capability to click a business interface also does not grant an agent permission to access every enterprise system.
OIDC sign-in uses existing corporate identity providers
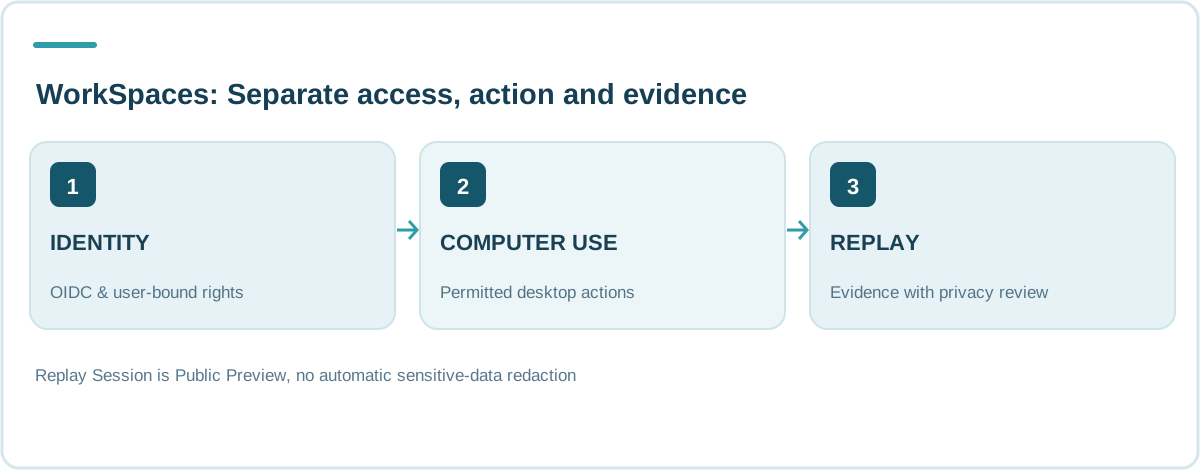
AWS adds OpenID Connect (OIDC) support for identity providers alongside existing SAML flows. Administrators can route sign-ins through an organization's established identity system and use its access policies instead of creating a separate sign-in mechanism solely for agents. That can simplify adoption in businesses with existing groups and centrally managed user rights.
This should not be confused with the separate MCP OAuth connection flow previously documented for developers. OIDC user authentication and OAuth authorization of an agent's connection address different boundaries. Both need appropriate configuration and auditability in AWS and in downstream business applications.
On-behalf-of access ties activity to a user's permissions
With on-behalf-of (OBO) sign-in, an eligible agent works as the signed-in user, inheriting that user's directory identity, desktop permissions and relevant group policies. That may be safer and more auditable than giving every automation a common high-privilege administrator account.
OBO does not confer unlimited rights over third-party services or business transactions. Applications may impose extra authentication, technical scopes or contractual rules. Organizations should separate viewing, drafting and irreversible actions and require explicit review for important decisions.
Integrating Claude Code, Codex, Kiro and AgentCore
AWS also describes workflows where coding assistants such as Claude Code, Codex and Kiro use AWS MCP skills to prepare a managed desktop. Developers using Amazon Bedrock AgentCore can connect suitable existing agents through the documented managed integration. AWS additionally highlights tools for batching several computer-use actions within a single call.
Reducing connection boilerplate and model calls can improve developer efficiency, but bundling actions does not establish safe execution. Policy boundaries, error handling and approvals must still cover each meaningful operation, especially when a batch crosses from observation into changing business records.
Replay Session reconstructs an agent's actions
Replay Session collects screenshots of the entire screen before agent actions alongside metadata about tools and inputs. After the session, AWS uses Bedrock to generate a replayable sequence, an AI-produced transcript and an HTML report, delivered to a customer-controlled Amazon S3 bucket. The result can aid debugging, post-hoc review and compliance evidence.
According to the technical guide, this capability is Public Preview, disabled by default and available for configured stacks rather than image builders. It is built from captured action frames, not a continuous recording of every screen frame. Post-event visibility helps investigations but does not prevent an unsafe action from happening.
Privacy: No automatic redaction and cross-Region processing
The session evidence may capture everything visible on screen, including personal records and confidential documents. Text typed by the agent appears in metadata and may be included in the transcript. AWS explicitly states that Replay Session performs no automatic redaction of sensitive information. Therefore retention, access controls and safe storage are critical.
AWS uses Amazon Bedrock cross-Region inference to produce the generated transcript. For the listed European session regions, inference is routed within Europe rather than necessarily staying in the same AWS Region. Some regions outside those supported geographic profiles can use global routes. The deployment owner must assess data residency and regulatory requirements before enabling the feature.
Image builders make privilege testing easier
In a separate November 16 AWS launch, WorkSpaces for AI Agents became available on WorkSpaces Applications image builders. Teams can test and refine their agent while preparing a desktop image, before deploying the final fleet and stack. The built-in TEST_USER account is useful for checking whether workflows work without administrator privileges.
New tools including `switch_user` and `get_current_user` allow controlled movement between user contexts during testing. This helps identify cases where an agent succeeds only because it has excessive privileges. Test outcomes still need to be reproduced on the production systems and permissions intended for users.
AgentenCode assessment: Governance before and after action
The strategic value of Amazon's announcement is not simply that a model can operate desktop software. It is the possibility of doing so through managed identities, constrained environments and reviewable outcomes, even when a legacy application has no usable API. Those controls address the gap between agent demos and accountable enterprise deployment.
Our guide to computer use and browser agents and AI-agent security explains these boundaries. Replay evidence alone is not an independent safety audit; it records selected steps after they occur. Safe autonomy needs enforced permission checks before an action and verifiable outcomes afterward.
Frequently asked questions
What changed in Amazon WorkSpaces for AI Agents?
AWS announced OIDC sign-in, user-bound OBO identities, Replay Session and additional setup and test integrations on November 16, 2026.
Is Replay Session generally available?
No. The AWS technical documentation labels it Public Preview, and administrators must enable it on supported stacks.
Are sensitive data automatically redacted from recordings?
No. Screen content and typed text may be recorded without automatic redaction.
Can an agent bypass enterprise permissions?
No. AWS, desktop, application and user access controls continue to apply; consequential operations need appropriate approval.
RESEARCH & CONTEXT
Sources for this article
This analysis relies on the original publications linked below, which readers can inspect directly.
- AWS What's New — Set up, connect, and govern AI agents faster with Amazon WorkSpaces (16 November 2026)
- AWS — WorkSpaces for AI Agents available on WorkSpaces Applications image builders (16 November 2026)
- AWS — Session evidence and Replay Session, feature status and privacy considerations
- AWS — WorkSpaces for AI agents adds Linux, Windows 11 and OAuth support (13 November 2026)
Checked November 17, 2026. Vendor statements, pilot scope and preview benchmarks have not been independently reproduced or certified.